Jason Nickerson — Hosting Industry InsiderTwo decades
inside the web
as it kept rewriting
itself.
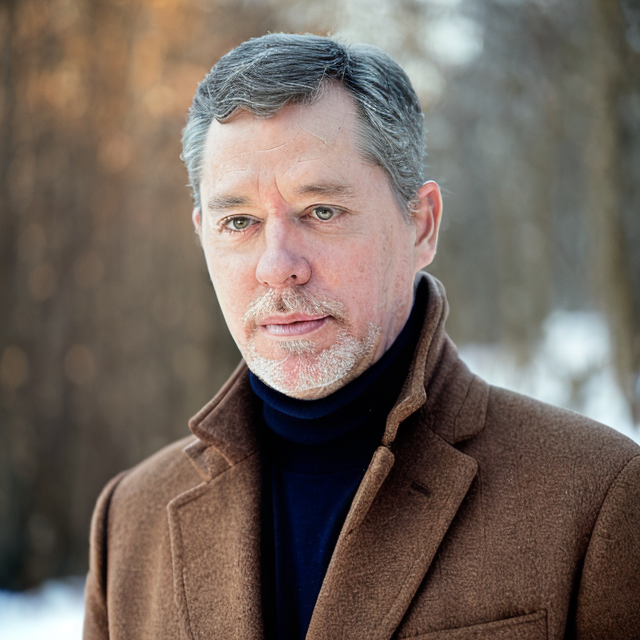
I’m Jason, a hosting industry insider with experience across open-source CMS platforms, control panels, cloud infrastructure, and the events that bring the industry together. Today, I focus on building partnerships, programming industry summits, and documenting what is happening across the hosting ecosystem.
- Oct 25, 2026
The Danger of a Single Point of Failure in Geopolitics
When the backbone of a nation's communication rests in one man's hands, the word 'redundancy' takes on an entirely new meaning.
Read article: The Danger of a Single Point of Failure in Geopolitics→ - Oct 24, 2026
Why Daytona’s $1B Agent Cloud is the Hosting Industry’s New Mirror
Daytona just hit a billion-dollar valuation by building a cloud for agents, proving that the future of hosting isn't just serving people, but the autonomous bots doing the work for us.
Read article: Why Daytona’s $1B Agent Cloud is the Hosting Industry’s New Mirror→ - Oct 24, 2026
The Undying Dominance of .com in a World of Alternatives
Verisign's latest numbers prove that despite the noise of new TLDs, the classic .com and .net extensions remain the bedrock of the global internet economy.
Read article: The Undying Dominance of .com in a World of Alternatives→


The early 2000s were the good years for tinkerers. Open-source CMS platforms were the closest thing we had to a universal starter kit, and PHP-Nuke and osCommerce were how you learned to ship real projects on the open web. I went deep on Joomla for the better part of a decade, contributing code to the project, organizing its community around releases and events, and eventually crossing over into the WordPress orbit that quietly swallowed everything in its path.
From there the story is a tour of the hosting stack: cPanel and the control-panel era that defined shared hosting, the managed cloud wave at Cloudways and DigitalOcean, and the publishing side at webhosting.today. Day to day now I'm at JetBackup, working on backup and disaster recovery and helping hosts protect the infrastructure that keeps everything running. I also program the seasonal industry summits, Atlas Digital Summit and Domain Days Dubai, where the hosting community gathers to set the agenda for what comes next.
The through-line is community, the conferences, the hallway conversations, and the group chats where the industry actually decides what happens next. The technology changes; the people pointing it in the right direction stay the same.
Twenty-something years,
in reverse.
- 2026 – present
 FounderAtlas Digital Summit
Private gatherings for hosting leaders, AI infrastructure innovators, and the builders of the agentic web.
- 2026 – presentFounderConf64
The Conference Operating System for Business Development and Field Marketing Teams.
- 2026 – present
 Co-FounderSuperDeploy
The advanced migration engine for AI applications. Seamlessly transition your codebase to independent, production-grade infrastructure in minutes.
- 2025 – 2026Director of Business Developmentwebhosting.today
Contract · Business development and partnerships for the hosting publisher.
- 2024 – presentBusiness Development & Partnerships ManagerJetBackup
Backup and disaster recovery for the hosting ecosystem.
- 2023 – present
 Chief Marketing Officer, Founding TeamDomain Days Dubai
MENA’s domain and digital asset conference.
- 2021 – 2023Senior Manager, WordPress Business Unit → Lead Community Marketing Manager IICloudways / DigitalOcean
Full-time · WordPress community, field marketing, and sales enablement through the acquisition.
- 2019 – 2021Marketing ManagercPanel
Full-time · Event planner and marketing strategist for 500–3,000 attendee events and virtual series.
- 2017 – 2019FounderCMS Summit
The global CMS conference.
- 2007 – 2019CEO | FounderJoomlaxtc.com / Monev Software LLC
Premium Joomla templates and extensions. 101,000+ members.
- 2015 – 2019Board Member, Capital Team ChairJoomla! Project
Leadership, sponsorships, and partnerships for the open-source CMS.
- 2001 – 2005DeveloperPHP-Nuke · osCommerce era
First shipping code in the early open-source web.


Threat Briefing: PHP-ocalypse Exploits, cPanel Mass-Scanning & WordPress Plugin Injection
1. INFRASTRUCTURE: Critical PHP RCE & cPanel Mass-Scanning
The "PHP-ocalypse" event has escalated as active exploitation data confirms two dormant vulnerabilities are now being targeted at scale [1, 5]. Shadowserver reports over 550,000 servers remain potentially vulnerable to cPanel/WHM-related RCE [7]. Attackers are utilizing leaked zero-day details to integrate these flaws into automated botnets [5].
Mass Exploitation of PHP-FPM / cPanel Environments — Remote Code Execution
- CVE / severity: CVE-2026-109618 and CVE-2026-41940 / CVSS 9.8 (Critical) [6, 7]
- Affected versions: PHP versions on Windows and specific cPanel/WHM versions (ea-php and alt-php binaries) [6, 9]
- Fixed in: PHP emergency patches (Oct 23/24) and cPanel security releases [7, 9]
- Action now:
- Run the following check on cPanel servers:
for b in /opt/alt/php[0-9]*/usr/bin/php /opt/cpanel/ea-php*/root/usr/bin/php; do [ -e "$b" ] || continue; p=$(rpm -qf "$b"); rpm -q --changelog "$p" | grep -q 'CVE-2026-109618' && echo "$p: FIXED" || echo "$p: NOT FIXED"; done[6] - Update via:
dnf updateor/scripts/upcp[6] - Restart services:
/scripts/restartsrv_apache_php_fpmand/scripts/restartsrv_httpd --stop && /scripts/restartsrv_httpd --start[6]
- Run the following check on cPanel servers:
2. WORDPRESS & CMS: Object Injection & Supply Chain Risks
A new critical deserialization flaw has been identified in the Paytium plugin, which can lead to PHP Object Injection, while 50,000 sites remain exposed to RCE through an unpatched backup plugin [4, 9].
Paytium Plugin Object Injection — Potential Remote Code Execution
- CVE / severity: CVE-2026-114196 / Severity not disclosed (High/Critical) [4]
- Affected versions: Paytium <= (All versions prior to current release) [4]
- Fixed in: Not disclosed in sources; check for latest plugin update [4]
- Action now:
- Update plugin:
wp plugin update paytiumimmediately. - Audit site for unauthorized administrator accounts or suspicious
.phpfiles inwp-content/uploads.
- Update plugin:
3. SUPPLY CHAIN: LiteLLM Backdoor & Python Package Poisoning
Security researchers discovered a master key leak for LiteLLM that allowed attackers to steal GitHub tokens and compromise a PyPI release, leading to a backdoor installation on servers using these AI-integration tools [8].
LiteLLM Master Key Leak — Data Theft & Backdoor Installation
- CVE / severity: No CVE assigned / Critical [8]
- Affected versions: Infrastructure using LiteLLM with exposed master keys; specific poisoned PyPI packages [8]
- Fixed in: Master key revocation by vendor [8]
- Action now:
- Rotate all GitHub tokens and credentials that may have been stored in LiteLLM environments [8].
- Verify integrity of Python environments:
pip listand check for unauthorized packages or versions released in the last 48 hours.
4. WINDOWS SHELL: Active Zero-Day Exploitation
Microsoft has issued an emergency patch for an actively exploited zero-day vulnerability in the Windows Shell, bypassing critical security features [12]. CISA has added this to the Known Exploited Vulnerabilities (KEV) catalog [10].
Windows Shell Security Feature Bypass — Active Zero-Day
- CVE / severity: CVE-2026-96951 / Severity Critical [12]
- Affected versions: Windows Server 2019, 2022, and 2025; Windows 10/11 [12]
- Fixed in: October 2026 Security Updates [12]
- Action now:
- Apply Windows Updates immediately via WSUS or Windows Update [12].
- Monitor for unusual
explorer.exeorcmd.exechild processes initiated via web browsers or mail clients.
On the
road.
Conferences, summits, and WordCamps I’ll be at in the months ahead.
- Nov 11 – 12, 2026
- State of the WordDec 2026
- Mar 15 – 18, 2027
When the servers
go quiet.
A small digital label putting out industrial house, progressive house, and dubstep. A different kind of open protocol.
Twenty years of showing up for the projects, communities, and voices that keep the open web open.
A news portal covering the hosting and domain industry — and a running excuse to keep talking to the people who build it.